Key Notes
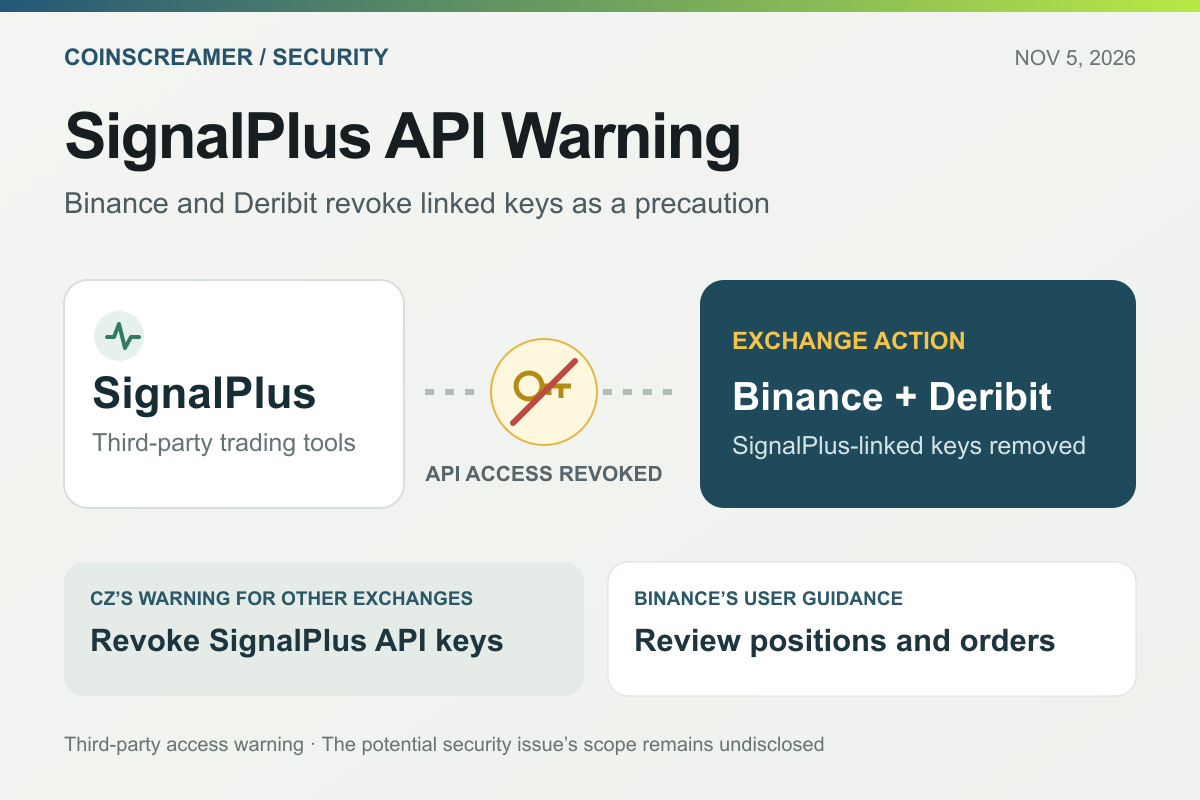
- Binance and Deribit removed SignalPlus-linked API keys as a precaution after a potential security issue.
- CZ urged SignalPlus users on other exchanges to revoke the platform’s API access.
- Binance says its systems and user funds are safe and advises reviewing positions before reconnecting.
SignalPlus users have been urged to revoke the platform’s access to their cryptocurrency exchange accounts after Binance and Deribit removed linked API keys in response to a potential security issue. Binance founder Changpeng Zhao extended the warning to customers using SignalPlus on other exchanges.
Binance’s November 5 security notice described the removals as a precaution following a report from the third-party platform. The exchange said its own systems were unaffected and user funds remained safe.
Exchanges Cut Connections as a Precaution
Binance asked affected customers to log directly into their exchange accounts and review positions and open orders. The instruction is particularly relevant to traders who had been managing activity through SignalPlus’s separate interface.
Deribit also removed SignalPlus-linked keys and said an investigation found no indication that its systems or data had been affected, Reuters reported. The report described SignalPlus as a digital-asset options and derivatives trading infrastructure platform.
The exchanges’ statements establish that connections were disabled. They do not establish that every connected account was compromised, or disclose a confirmed loss figure or a technical explanation of the potential issue.
CZ Warns Users on Other Exchanges
“If you use SignalPlus for any other exchange platform, it’s time to revoke all your API keys,” Zhao wrote on X. He also advised against storing exchange API credentials with third-party platforms.
His warning concerns the keys entrusted to SignalPlus, including connections outside Binance and Deribit. Users of other exchanges should check those accounts directly rather than assume the two exchanges’ actions have removed access elsewhere.
API keys let an external application interact with an exchange account within the permissions granted to it. Deribit’s partner documentation, for example, separates account, wallet and trading permissions and distinguishes read access from read-and-write authority.
That distinction explains why an API key is sensitive even though it is not a wallet seed phrase. A connection authorized to submit orders carries different risks from one limited to viewing information. The permissions on an individual key matter; access should not be treated as identical across every integration.
Review Positions Before Reconnecting
Binance recommended waiting until SignalPlus confirms a full resolution before rebinding keys, and enabling IP whitelisting for API connections. Whitelisting restricts where requests can originate, adding a control alongside the key’s permissions.
For affected traders, checking account access and checking market exposure are separate tasks. Binance’s instruction to review positions and orders should not be interpreted as confirmation that removing an API key has also closed trades or canceled every outstanding order.
The warning follows October’s Binance attack, which the exchange attributed to a chain of employee-device and wallet-signing compromises. The latest notice concerns third-party API access; the statements reviewed do not establish a connection between the two incidents.
CoinScreamer’s earlier security coverage examined how vendor incidents can expose different parts of a financial service. Here, Binance has also asked integration partners to review controls, monitor unusual activity and promptly report concerns.
Disclaimer: CoinScreamer is an independent media brand owned and operated by NuvexMedia LLC, publishing news, research, and market insights on digital assets and related technologies. NuvexMedia LLC invests in and collaborates with companies across the digital asset, blockchain, and technology sectors. These relationships do not influence CoinScreamer’s editorial coverage, and the publication maintains full editorial independence to provide accurate, timely, and objective information. © 2025 NuvexMedia LLC. All rights reserved. This content is for informational purposes only and should not be considered legal, tax, investment, financial, or other professional advice.